Scanity
A security review tool aimed at vulnerabilities in AI-generated code and pull requests.
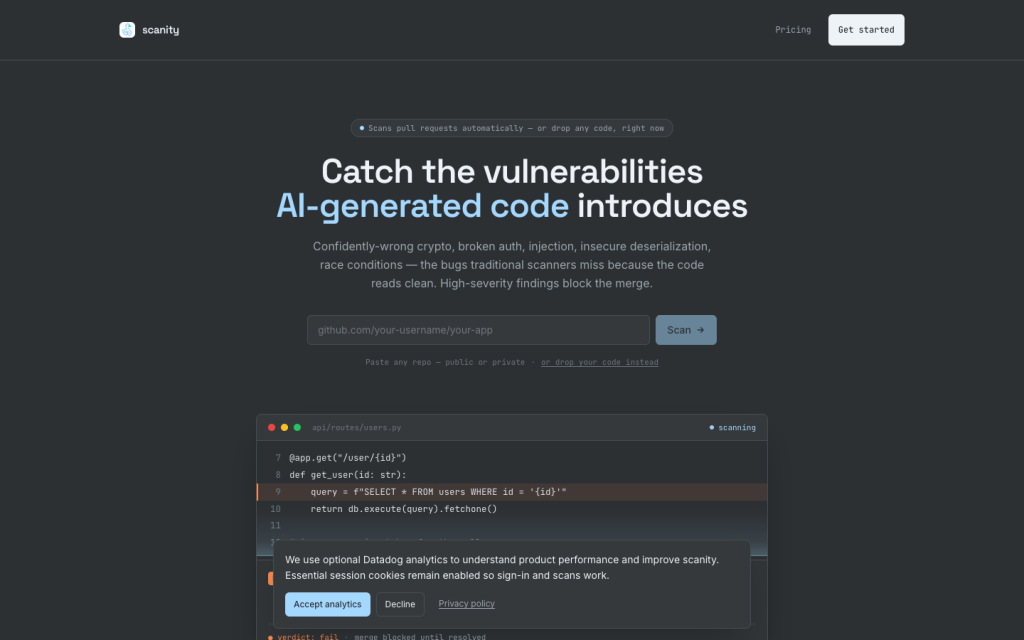
A Scanity maker mentioned the project in a September 1, 2026 Reddit build thread. The current site frames it as a security review tool for code that may look plausible while hiding errors introduced with AI assistance.
From pull request to merge gate
Scanity's described flow begins when a pull request opens or changes: a webhook queues a scan, the service examines the code and returns findings. The homepage demonstrates a SQL-injection example and says high-severity findings can block a merge. It also advertises whole-repository scans, so an older file is not excluded simply because the latest pull request left it untouched.
Who is building it
The site's team page credits Ayman Ahsan with model training, backend services and data work, and Dihyah Adib with the frontend, infrastructure, billing and authentication. That is more concrete than a generic claim that the tool is ‘AI-powered,’ but it does not establish how accurately the scanner performs on real repositories.
What can be concluded today
There is a live site and an inspectable product demonstration. Neither the Reddit comment nor the site's public material supplied a customer count, revenue figure or independent detection benchmark. Its comparison with established scanners remains a product claim until tested independently.
Sources: the maker's Reddit build update; Scanity's product and team page.
Homepage screenshot captured by CoderHype for this independent editorial listing.
CoderHype Score
A quick way to compare projects on CoderHype. Scores can change over time.
Log in to rate this project.
Is this your project?
We listed this project to help people discover it. If you made it, send us a claim and we can put it under your CoderHype account after checking your connection to the project.